

Port scanning is a technique used to identify open ports on a computer or network. These open ports may provide hackers and other cybercriminals with a way to break into systems. By identifying open ports, they can discover vulnerabilities that can be exploited. This article will explain in detail what port scanning is, how it works, and how to effectively prevent port scanning.
What Is Port Scanning?
Port scanning is the process of probing a network host for open ports to discover available services and assess security vulnerabilities. It involves sending information to individual ports on a network device and analyzing the responses to determine the status of each port.
The primary purpose of port scanning is to identify which ports are open and listening for incoming connections. This information can be used legitimately by network administrators, but it may also be maliciously exploited by cybercriminals.
Port scanning typically involves the following protocols:
TCP (Transmission Control Protocol)
UDP (User Datagram Protocol)
TCP is a connection-oriented protocol that ensures reliable data transmission by establishing a connection between the sender and receiver, providing error checking, and ensuring that packets arrive in the correct order.
In contrast, UDP is a connectionless protocol that can send data without establishing a connection, making it faster but less reliable because it cannot guarantee data delivery, ordering, or error recovery.
How does port scanning work?
Port scanning works by systematically probing a target system to identify open ports and the services associated with them.
Target selection: The user specifies the target IP address or hostname to scan, which can be a single device or a range of devices on the network.
Scan type selection: The user selects the type of port scan to perform based on the scanning software being used. Each scan type has its own unique method and level of stealth.
Packet transmission: The scanning tool sends packets to the specified ports on the target system.
Response analysis: The scanning tool listens for responses from the target system.
Service detection: If a port is determined to be open, the scanning tool may send additional probes to gather information about the service running on that port, such as HTTP or FTP, and its version.
Operating system fingerprinting: Some advanced scanners may analyze response characteristics using techniques such as TCP/IP stack fingerprinting to infer the target's operating system.
Results compilation: After the scan is complete, the tool compiles the results, providing a list of open ports, associated services, and other information collected during the scan.
Report Generation: Finally, the scanning tool generates a report summarizing the scan results. This report can be used for security assessments, vulnerability analysis, or network management.
Types of Port Scanning Techniques
Port scanning software can use several basic techniques to identify open ports and the services running on them. Some common techniques include:
TCP Connect Scan
This technique attempts to establish a complete TCP three-way handshake (SYN, SYN-ACK, ACK) with each port. If the connection succeeds, the port is open; if the connection fails, the port is closed.
However, this method is easy to detect because it completes the full TCP handshake process.
SYN Scan
Also known as a half-open scan, this technique sends a SYN packet to the port (to initiate a TCP connection). If a SYN-ACK response is received, the port is open; if an RST response is received, the port is closed.
This scan is more stealthy than a TCP connect scan, and attackers commonly use it to evade detection.
UDP Scan
UDP scanning works differently from TCP scanning because it uses the User Datagram Protocol. If an ICMP “port unreachable” message is received, the port is considered closed; if there is no response or a different type of response is received, the port is considered open.
Because no connection is established, UDP scanning is generally slower and less reliable than TCP scanning. It is commonly used to scan services that run over UDP, such as DNS and SNMP.
FIN scan
This method sends FIN packets to ports. According to the TCP specification, closed ports should respond with RST packets, while open ports should ignore FIN packets.
This method is used to stealthily check for open ports because it can sometimes bypass firewalls and intrusion detection systems that do not log FIN packets.
Xmas scan
Named after the alternating TCP header flags, this technique sends packets with the FIN, URG, and PUSH flags set.
Similar to a FIN scan, closed ports should respond with RST packets, while open ports will ignore the packet.
How do cybercriminals use port scanning to launch attacks?
Port scanning is a fundamental technique used by cybercriminals to identify vulnerabilities in target systems.
Attackers first gather information about the target network, including identifying IP addresses and network ranges. They then use port scanning tools to perform an initial scan and detect which ports are open and available.
Once open ports have been identified, attackers probe them to determine which services and applications are running. They may use database vulnerabilities or automated tools to determine the best way to exploit these weaknesses.
When port scanning is used successfully, it can lead to serious consequences, including:
Unauthorized access
Data breach
System crash
How to scan ports?
You may wonder: if port scanning is commonly used by cybercriminals for malicious purposes, why scan ports at all? The answer lies in proactive security maintenance. By scanning ports, you can identify and secure them before attackers exploit open ports. Regular port scanning helps you understand network vulnerabilities, enabling you to take preventive measures and strengthen your overall security posture.
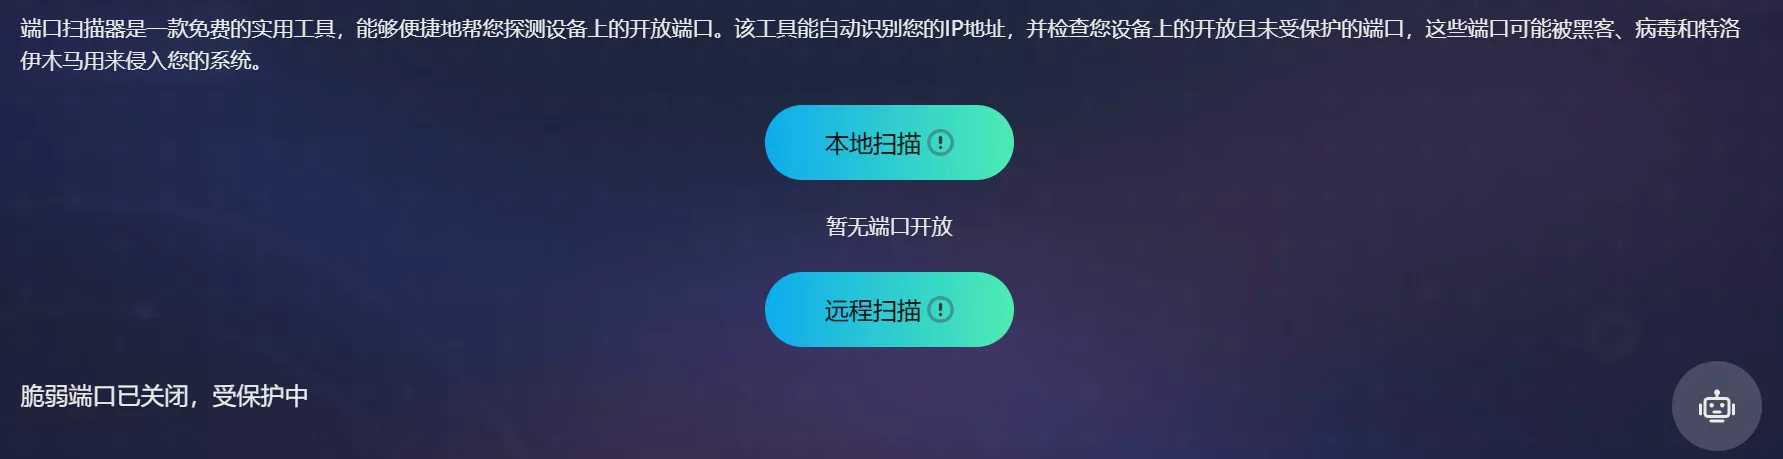
With the P1Browser port scanner, you can proactively identify and mitigate risks, ensuring network security.
P1Browser can automatically detect a device's IP address, eliminating the need for manual entry. Once the IP address is detected, P1Browser scans a range of ports to determine which ports are open and which may be unprotected. The port scanner checks for vulnerabilities that could be exploited by hackers, viruses, or Trojan horses.
How to Prevent Port Scanning?
Close Unnecessary Ports
One of the simplest and most effective ways to prevent port scanning attacks is to close unnecessary ports. This reduces the number of entry points available for attackers to exploit. Regularly review and update the list of open ports to ensure that only necessary services are exposed, thereby minimizing the risk of exploitation.
Use a Firewall
A firewall monitors incoming and outgoing network traffic according to predetermined security rules, helping to block unauthorized access while allowing legitimate communication.
Configure the firewall to allow only necessary traffic to enter specific ports and block all other traffic. This can be achieved through router settings or by using a software-based firewall on individual devices. Firewalls can also be configured to log suspicious activity and issue alerts, providing additional security protection.
Network Segmentation
By segmenting a network, you can limit an attacker’s ability to move laterally within the network after accessing one segment. This strategy helps prevent widespread damage.
Enable an Intrusion Detection System (IDS)
An IDS monitors network traffic for suspicious activity and known threats, issuing alerts when a potential intrusion is detected.
Many modern routers and security software packages include built-in IDS functionality. Make sure the IDS is enabled and properly configured to monitor the network.
Conclusion
Overall, by taking measures to prevent port scanning, you can effectively prevent vulnerabilities from being exploited by malicious attackers. Regularly scanning ports with online port scanning tools such as P1Browser and implementing the preventive measures described above will help maintain a secure and resilient network environment.
Common Questions About Port Scanning
What are the risks of port scanning?
Port scanning itself is not harmful, but attackers can use it to identify open ports and vulnerable services, thereby gaining unauthorized access, launching attacks, or disrupting systems.
Can port scans be detected?
Yes, intrusion detection systems (IDS) and firewalls can detect port scans. These systems can log scanning activity and issue alerts, helping you take appropriate measures to protect network security.
What free port scanning tools are available online?
You can use several free online port scanning tools, including:
Nmap: A versatile and widely used network scanning tool.
Angry IP Scanner: A fast and easy-to-use IP and port scanning tool.
P1Browser: An online port scanner that automatically detects IP addresses and checks for open and unprotected ports.
How often should I perform port scans?
It is recommended that you perform port scans regularly based on the size of your network and your security needs, such as once a week or once a month. In addition, you should perform a port scan after any major changes to the network or IT infrastructure.